
Cybersecurity Services In New York City
The firms getting breached in New York are not the ones you read about.
They are the twenty- and eighty-person offices that assumed they were too small to target. Our cybersecurity services in New York City put real, layered protection around your business, watched around the clock, documented for the auditors and insurers who now ask hard questions, and backed by a live engineer who answers in under 10 minutes when something looks wrong.
What Our New York Security Program Covers
The layered protection, monitoring, and documentation that keep your business out of the headlines.
Managed Detection & Response
Threats hunted and contained across every endpoint, with a response that starts in minutes, not the next business day.
24/7 SOC Monitoring
A security operations center watching your systems overnight, on weekends, and through every New York holiday.
Email & Phishing Defense
Filtering, impersonation protection, and staff phishing tests, because the inbox is still the front door for attackers.
Identity & Access (MFA)
Multi-factor authentication and least-privilege access on every account, so a stolen password is not a breach.
Security Awareness Training
Short, regular training that turns your team from the weakest link into the first line of defense.
Firewall & Network Security
Firewalls, segmentation, and traffic monitoring configured and maintained across every floor and site.
Vulnerability & Patch Management
The known holes attackers scan for, found and closed on a schedule instead of whenever someone remembers.
Incident Response Planning
A written plan agreed before anything happens, so the first hour of an incident is action, not panic.
Compliance & Audit Documentation
Controls mapped and documented for NYDFS 23 NYCRR 500, HIPAA, SOC 2, and cyber-insurance questionnaires.
What Clients say about 360 Networks
Why New York Firms Trust Us With Security
Watched Around The Clock
Attacks do not wait for business hours. Your systems are monitored overnight, on weekends and on holidays, by people, not just software.
Layered, Not One Magic Box
No single product stops every attack. We layer defenses across identity, devices, email, and network, so one failure is not a breach.
A Live Engineer In Under 10 Minutes
When an alert fires, a real engineer is on it in under 10 minutes, because in a live incident the first hour decides how bad it gets.
Clear Reporting, No Scare Tactics
You get plain reporting on what we see and fix, not a monthly threat-count designed to frighten you into spending more.
On-Site Across The Five Boroughs
When an incident needs hands-on work on a machine or a device seized, an engineer is on site the same day anywhere in the five boroughs.
Engineers Who Know Your Setup
The same team secures you month after month, working from documentation of your environment, so nothing unusual slips past unnoticed.
Documented For Auditors And Insurers
We put controls in place and keep the evidence current, so NYDFS filings, client questionnaires, and cyber-insurance renewals stop being a scramble.
You Are Not Too Small To Be A Target
A small office is not a small target. Attackers automate, and a thirty-person firm in Manhattan with a good bank balance and weak logins is exactly what their tools look for. We give businesses across New York enterprise-grade security run for them, so you are protected without hiring a security team you cannot justify.
Protection You Do Not Run
We configure, monitor, and maintain it, so security is handled rather than added to someone’s job.
Insurance You Can Actually Get
We put in the controls insurers now require, so coverage is approved, and claims hold up.
Training That Sticks
Short, regular sessions your staff will actually absorb, not a once-a-year slideshow.
Costs You Can Budget
Security delivered on a predictable monthly basis, with no surprise project invoices.
The Security Scrutiny New York Enterprises Face
New York’s financial, legal, and healthcare organizations face the sharpest scrutiny in the country, from NYDFS examiners, from clients with their own security teams, and from attackers who know where the money and the records sit. We hold every location to one security standard with one team accountable, so a gap in a satellite office is never the way in.
One Standard Everywhere
The same controls, monitoring, and response in every office, from headquarters to the smallest site.
Audit-Ready At All Times
NYDFS, HIPAA, and SOC 2 evidence kept current, not assembled in a panic before a deadline.
Coverage Around The Clock
A SOC staffed for overnight desks and weekend operations, matching how New York actually works.
Growth Handled Securely
New locations and acquisitions brought up to your standard from day one, not months later.
Not Sure Where Your Gaps Are?
Most breaches start with something small and known. Ask us for a free security assessment of your New York business, and we will show you where the real exposure is and reply within one hour.
Get A Security Assessment
How We Actually Protect You
Here is what each layer of our cybersecurity services in New York City actually protects, how our team runs it, and where it connects to the rest of your IT.
24/7 SOC Monitoring
Attacks do not keep office hours. Our SOC monitoring in New York watches your environment around the clock, so managed cybersecurity in New York means a real analyst is looking when something fires at 3 a.m.
- Round-the-clock eyes on your environment
- Alerts triaged by analysts, not just logged
Identity And Access Security
Most breaches are really stolen logins. As an IT security company in NYC, we lock down identity with MFA, conditional access, and least-privilege, so one phished password does not open everything.
- MFA and conditional access enforced
- Least-privilege access, reviewed regularly
Security Awareness Training
Your people are the layer attackers target first. Our cybersecurity NYC training turns staff into a line of defense with short, regular sessions and real phishing tests.
- Short, regular training that sticks
- Phishing tests with coaching, not blame
Vulnerability And Patch Management
Unpatched systems are the open door. Our cybersecurity services NYC find and close vulnerabilities on a schedule, the kind of discipline a real cybersecurity MSP / MSSP NYC runs by default.
- Vulnerabilities found and ranked by risk
- Patching on a schedule, not when there is time
Managed Detection And Response
Antivirus alone stopped being enough years ago. Modern attacks live off legitimate tools and move quietly, so by the time anything looks wrong, the attacker has been inside for weeks. Our managed detection and response (MDR) NYC watches behavior across every device in New York, flags what does not belong, and contains it before it spreads.
- Endpoint detection on every laptop, desktop, and server
- Threats contained automatically, then reviewed by an engineer
- Built on the same monitoring behind our managed IT services in New York City
Backup, Recovery, and Ransomware
The point of ransomware is to make your data unusable until you pay. The defense is recovery you have actually tested, kept separate from the systems an attacker can reach. Our ransomware protection in New York pairs security monitoring with proven restores, so a ransomware demand becomes a bad afternoon instead of a closed business.
- Immutable backups an attacker cannot encrypt
- Restores tested on a schedule, through our backup and disaster recovery in New York City
- A recovery plan with real target times per system
Email Security And Phishing Defense
Most breaches in New York start with one convincing email. A finance clerk approves a fake invoice, or a partner clicks a login page that is not real. We filter the obvious threats, flag the impersonation attempts that get through, and test your team with safe phishing simulations so the real one gets reported instead of clicked.
- Advanced filtering and impersonation protection
- Staff phishing tests with coaching, not blame
- Tightened inside your Microsoft 365 management tenant
Compliance, NYDFS And Cyber Insurance
For financial and professional firms in New York, security is also a paperwork problem. NYDFS 23 NYCRR 500 expects named controls and annual certification; clients send security questionnaires, and insurers decline claims when the controls on the application were never really in place. Our NYDFS compliance IT puts the controls in, documents them, and keeps the evidence ready.
- Controls mapped to NYDFS Part 500, HIPAA and SOC 2
- Questionnaire and insurance-application answers prepared
- A breach-response plan aligned with New York notification rules
NYDFS 23 NYCRR 500 Compliance For New York Financial Firms
If your business is licensed by the New York Department of Financial Services, Part 500 is not optional, and the deadlines keep tightening. It expects a named CISO function, multi-factor authentication, encryption, a written incident-response plan, annual penetration testing and vulnerability assessments, and a signed certification of compliance each year. For a mid-sized firm without a security team, that list is daunting. We make it manageable.
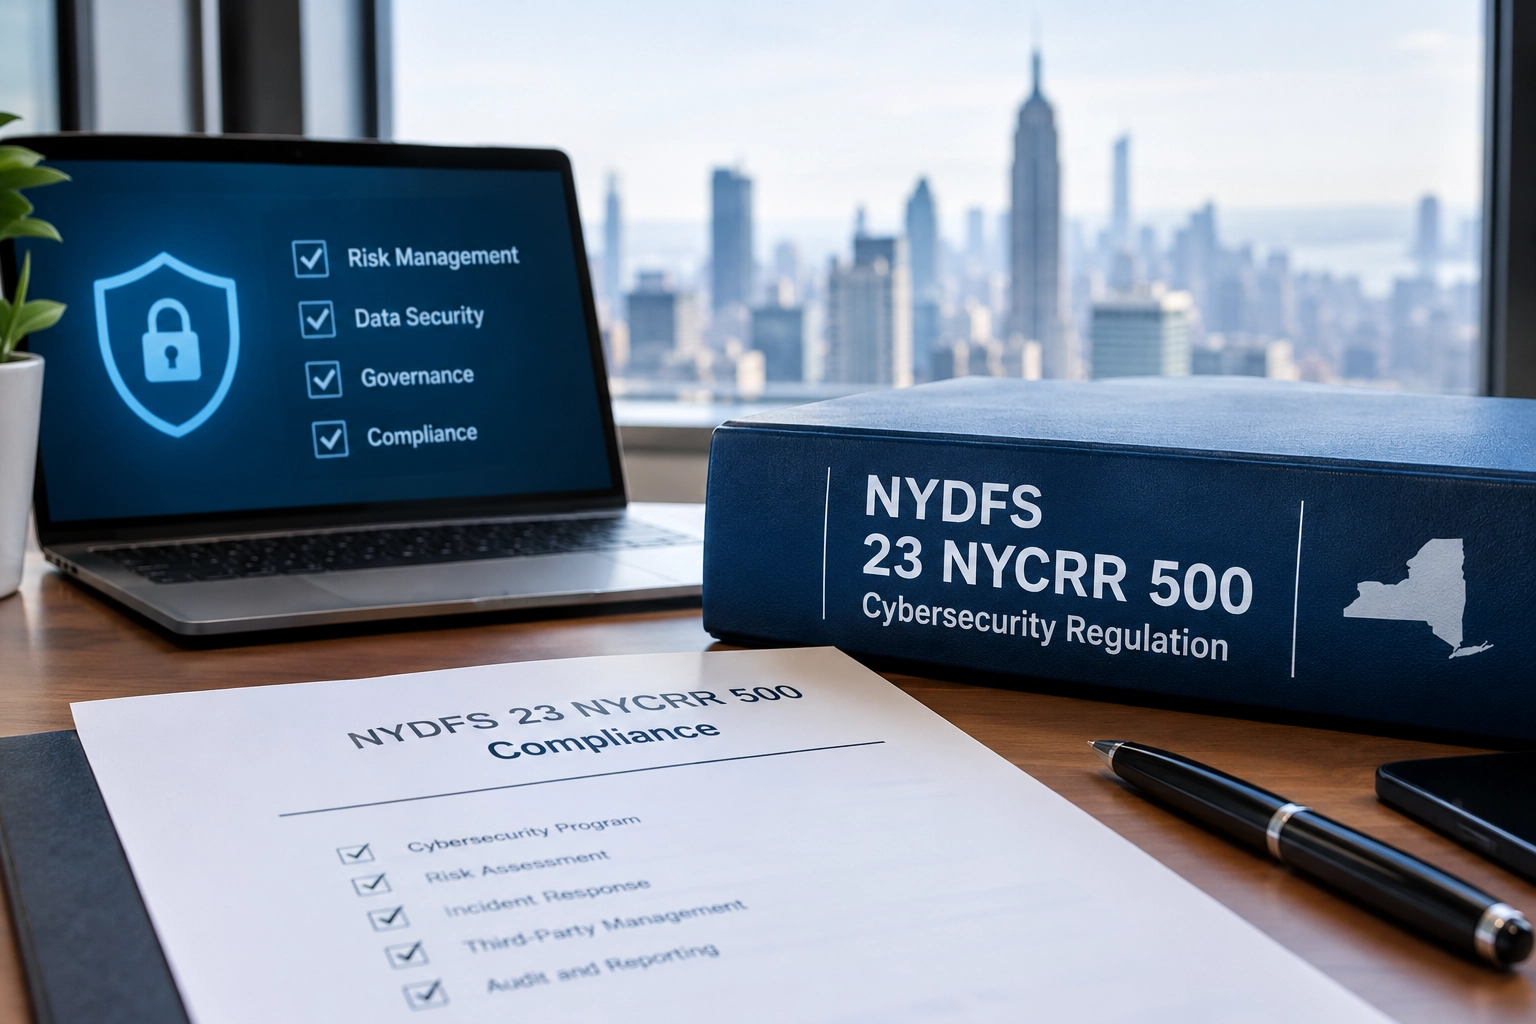
We run a gap assessment against the current rule, put the missing controls in place, and keep the evidence current, so your annual certification is honest. If an incident ever triggers the 72-hour notification requirement, you already have the plan and the documentation to meet it. The result is a filing you can sign without crossing your fingers, built into the same security program that protects you day to day.
- Gap assessment mapped to every Part 500 requirement
- CISO function, MFA, encryption, and incident response covered
- Annual penetration testing and vulnerability assessments arranged
- Evidence kept current for the yearly certification and any 72-hour notice
Layered defense, documented for NYDFS, insurers, and your clients.
A Team Keeping You Out Of The Headlines
Security is not a product you buy once. It is a program somebody has to run every day, keep current as threats change, and prove when an auditor or insurer asks. That is what our cybersecurity services in New York City are: not a box on a shelf, but a team accountable for keeping your business out of the headlines.
360 Networks protects law firms, financial and insurance offices, medical and life-science teams, and the professional firms that hold data worth stealing across New York. We document the controls that NYDFS 23 NYCRR 500, HIPAA, and cyber insurers ask for, and we are hardware- and software-agnostic, so we secure what you already run. For the full picture, see our managed IT services in New York City and our network and infrastructure management.
Security Coverage Across New York
We secure businesses on-site and remotely across Manhattan, Brooklyn, Queens, the Bronx, and Staten Island, from financial offices in the Financial District and Midtown to practices and firms throughout the outer boroughs, and out into the wider metro including Yonkers and White Plains. For coverage beyond the city, see our cybersecurity and managed IT across New York State.
Certified Partners


Frequently Asked Questions About Cybersecurity Services In New York City
What do cybersecurity services include for a business in New York City?
Cybersecurity services are the ongoing protection of your systems, accounts, and data against attack. For businesses in New York City, 360 Networks provides managed detection and response, 24/7 SOC monitoring, email and phishing defense, multi-factor authentication, security awareness training, firewall and network security, vulnerability management, incident response planning, and the compliance documentation that NYDFS, HIPAA, and cyber insurers require. A live engineer responds in under 10 minutes, with same-day on-site service anywhere in the five boroughs.
Is my business too small to be a target in New York?
No, and that assumption is why small firms get hit. Most attacks are automated and look for weak logins and unpatched systems, not big names. A twenty- or fifty-person business in New York with money to move and limited defenses is an easy target. Our cybersecurity services give smaller firms the same layered protection larger ones have, run for you so you do not need an in-house security team.
Can you help us meet NYDFS 23 NYCRR 500 (Part 500)?
Yes. NYDFS Part 500 applies to a wide range of financial and insurance businesses in New York and expects named controls plus annual certification. We put the required controls in place, document them, support the risk assessment and policies, and keep the evidence ready, so your certification is based on reality, not a form someone signed hoping it was true.
Will this help us pass a cyber-insurance application or client security questionnaire?
Yes, this is one of the most common reasons businesses in New York come to us. Insurers and clients now ask detailed questions about multi-factor authentication, backups, monitoring, and training. We put those controls in place and prepare the answers, so your application is approved, your premium reflects real security, and a future claim is not denied over a control that was never actually running.
What happens if we get breached or hit with ransomware?
We act on the plan we agreed on before anything happened. Our team contains the incident, works to limit the damage, and starts recovery from backups kept out of an attacker’s reach, with an engineer on site in New York the same day if needed. Because recovery is tested in advance, a ransomware demand becomes a controlled recovery rather than a decision about whether to pay.
Do you replace our current IT team or work with them?
Either way. We can run security entirely for you, or work alongside your IT staff as the specialist security layer, handling monitoring, response, and compliance while they keep the day-to-day. Many firms in New York use us this way so their internal team is not on the hook for a 2 a.m. security alert.
How do cybersecurity services differ from regular IT support in New York?
IT support keeps your technology working. Cybersecurity keeps it from being used against you, and the two overlap but are not the same. Our cybersecurity services in New York City sit on top of day-to-day support, adding monitoring, threat response, compliance, and training. Many clients take both together through our managed IT services so one team owns both the uptime and the security.
Find The Gaps Before An Attacker Does
Security is a program somebody has to run every day, keep current, and prove when an auditor or insurer asks. That is what our cybersecurity services are: a team accountable for keeping your business safe.
- A live engineer on an alert in under 10 minutes
- Watched around the clock, by people, not just software
- Documented for NYDFS, HIPAA, and cyber insurers